Client Encryption Source (Tool + Hook DLL) - RSA1024/RC4 Source 

Joined
Jan 26, 2025
Messages
246
Reaction score
252
Hey everyone,

Today I'm releasing an encryption source code that I received from a developer friend in Vietnam last year. We used to share a lot of knowledge and experiences, but since disappeared from the scene (we lost contact). Because I miss the guy and the collaboration we had, I've decided to share this source with the community.

To be completely honest, back when we were talking, I was dealing with some heavy paranoia regarding real-life events and ended up misleading him a bit. (thats when i decided visit our be loved game. ) :) So, if you are still out there reading this, buddy—let's get in touch again. I have some good news for the Vietnamese community, so please hit me up.

If you've been around the scene, you will likely recognize this. It is widely used across both Chinese and English servers. Many servers have taken this base and modified it to create their own "custom" versions, but the core mechanics remain the same.

🛡️ A Reality Check on "Proprietary" Protection​

When we talk about proprietary client protection, the actual goal is just to make copy-pasting your assets a little more difficult. It keeps the kiddies away, but let's be realistic: it won't perform miracles against someone whos rly want reverse that.

So far, I have not encountered a single private server in this entire community where the client files couldn't eventually be unpacked. Sometimes it takes longer, but the result is always the same: fully unpacked files.

Because this specific hook decrypts files "on the fly" and drops them to the disk temporarily, someone who knows what they are doing will figure out the magic and grab your assets in about 10 minutes.

⚙️ What's Included & How it Works​

This is a two-part system written in C++:

  1. The Encrypter Tool: Packages your files (local, maps, ui, etc.).
  2. The Client DLL: Hooks CreateFileA to intercept file loads and decrypt them for the client.
  3. Algorithms: It relies on OpenSSL for 1024-bit RSA (to secure the headers/keys) and Windows CryptoAPI for RC4 (for bulk file data). It also features basic Anti-VM and Sandbox detection.

🛠️ Setup Instructions​

You can compile this easily using Visual Studio Community. Just make sure you link the required OpenSSL dependencies properly.

To make this build your own, you must change the following variables:

1. Generate and Replace the RSA Keys:You need to generate your own RSA-1024 key pair.

  • Open Decrypting_a_File.cpp and replace the private_key_str variable with your new private key.
  • Open Encrypting_a_File.cpp and replace the public_key_str variable with your new public key.
2. Match the Hardware/Session String:Both the encryption tool and the client DLL need to share the same base string to communicate properly.

  • Find #define STATIC_HDDSN "Ez*ajzO1gIu4W|{y+b^x+xN=~vhM:"
  • Change that random string to something unique, and ensure it matches perfectly in both the Tool source and the dllmain.cpp (local.dll) source.

⚠️ Pro-Tips for Packing​

Your magic and your security rely on your own personal secrets. You can split the keys into multiple pieces, modify the hook logic, etc.

However, do not pack the entire compiled DLL globally with a protector. If you throw the whole binary into Themida or VMP and just click protect, you are going to cause massive performance overhead and likely crash the client. Instead, you need to use a hybrid approach—target and virtualize/mutate only the specific, critical sections of the code that handle the key generation and decryption logic.

Note: I will not be providing support on how to pack or obfuscate your binaries.

I might provide a more detailed tutorial soon, but if you run into basic compilation problems, post them here and I can try to help you out.

1778386334253 - Client Encryption Source (Tool + Hook DLL) - RSA1024/RC4 - RaGEZONE Forums


1778386715316 - Client Encryption Source (Tool + Hook DLL) - RSA1024/RC4 - RaGEZONE Forums


💉 Injecting the DLL (CFF Explorer)​

For the client to actually use your new encryption hook, you need to force the game executable to load it on startup. We will do this by adding it to the client's Import Table.

Requirements: You will need CFF Explorer.


Instructions:

  1. Move your files: Once you compile the project, take your compiled DLL (e.g., local.dll or whatever you named it) and the OpenSSL dependency (libeay32.dll). Place both of them in the root folder of your game client, right next to your main client.exe
  2. Open CFF Explorer: Launch CFF Explorer and drag-and-drop your game client.exe into the program.
  3. Go to Import Adder: On the left panel, click on Import Adder.
  4. Add your DLL: Click the Add button and select your compiled DLL from the client folder.
  5. Import by Name: You will see a list of exported functions. Select the dummy export function (if you didn't change the source code, it should be called protect2024) (you can rename to whatever you want) . Select it, click Import By Name, and then click Add.
  6. Rebuild Import Table: Click the Rebuild Import Table button to finalize the injection.
  7. Save the Client: Go to File > Save (or click the save icon) and overwrite your client .exe.
Now, when you launch your game, it will automatically load your hook DLL, which will in turn load libeay32.dll and start intercepting and decrypting your file loads on the fly!

🛠️ Troubleshooting: "libeay32.dll is missing" Error​

If you try to launch your game and get a system error saying libeay32.dll is missing—even though you placed it right next to the .exe—don't panic. This just means the game executable isn't hooking the OpenSSL dependency automatically.

The Fix: You just need to force the client to load it using the exact same method we used for the hook.

  1. Open your client .exe in CFF Explorer again.
  2. Go to the Import Adder.
  3. Add libeay32.dll.
  4. Select any random exported function from the list, click Import By Name, and hit Add.
  5. Rebuild Import Table and save your .exe.
That's it! The client will now forcefully load the OpenSSL library, and your encryption hook will work perfectly.

📥

 
Last edited:
Hey everyone,

Today I'm releasing an encryption source code that I received from a developer friend in Vietnam last year. We used to share a lot of knowledge and experiences, but since disappeared from the scene (we lost contact). Because I miss the guy and the collaboration we had, I've decided to share this source with the community.

To be completely honest, back when we were talking, I was dealing with some heavy paranoia regarding real-life events and ended up misleading him a bit. (thats when i decided visit our be loved game. ) :) So, if you are still out there reading this, buddy—let's get in touch again. I have some good news for the Vietnamese community, so please hit me up.

If you've been around the scene, you will likely recognize this. It is widely used across both Chinese and English servers. Many servers have taken this base and modified it to create their own "custom" versions, but the core mechanics remain the same.

🛡️ A Reality Check on "Proprietary" Protection​

When we talk about proprietary client protection, the actual goal is just to make copy-pasting your assets a little more difficult. It keeps the kiddies away, but let's be realistic: it won't perform miracles against someone whos rly want reverse that.

So far, I have not encountered a single private server in this entire community where the client files couldn't eventually be unpacked. Sometimes it takes longer, but the result is always the same: fully unpacked files.

Because this specific hook decrypts files "on the fly" and drops them to the disk temporarily, someone who knows what they are doing will figure out the magic and grab your assets in about 10 minutes.

⚙️ What's Included & How it Works​

This is a two-part system written in C++:

  1. The Encrypter Tool: Packages your files (local, maps, ui, etc.).
  2. The Client DLL: Hooks CreateFileA to intercept file loads and decrypt them for the client.
  3. Algorithms: It relies on OpenSSL for 1024-bit RSA (to secure the headers/keys) and Windows CryptoAPI for RC4 (for bulk file data). It also features basic Anti-VM and Sandbox detection.

🛠️ Setup Instructions​

You can compile this easily using Visual Studio Community. Just make sure you link the required OpenSSL dependencies properly.

To make this build your own, you must change the following variables:

1. Generate and Replace the RSA Keys:You need to generate your own RSA-1024 key pair.

  • Open Decrypting_a_File.cpp and replace the private_key_str variable with your new private key.
  • Open Encrypting_a_File.cpp and replace the public_key_str variable with your new public key.
2. Match the Hardware/Session String:Both the encryption tool and the client DLL need to share the same base string to communicate properly.

  • Find #define STATIC_HDDSN "Ez*ajzO1gIu4W|{y+b^x+xN=~vhM:"
  • Change that random string to something unique, and ensure it matches perfectly in both the Tool source and the dllmain.cpp (local.dll) source.

⚠️ Pro-Tips for Packing​

Your magic and your security rely on your own personal secrets. You can split the keys into multiple pieces, modify the hook logic, etc.

However, do not pack the entire compiled DLL globally with a protector. If you throw the whole binary into Themida or VMP and just click protect, you are going to cause massive performance overhead and likely crash the client. Instead, you need to use a hybrid approach—target and virtualize/mutate only the specific, critical sections of the code that handle the key generation and decryption logic.

Note: I will not be providing support on how to pack or obfuscate your binaries.

I might provide a more detailed tutorial soon, but if you run into basic compilation problems, post them here and I can try to help you out.

View attachment 300926

View attachment 300928

💉 Injecting the DLL (CFF Explorer)​

For the client to actually use your new encryption hook, you need to force the game executable to load it on startup. We will do this by adding it to the client's Import Table.

Requirements: You will need CFF Explorer.


Instructions:

  1. Move your files: Once you compile the project, take your compiled DLL (e.g., local.dll or whatever you named it) and the OpenSSL dependency (libeay32.dll). Place both of them in the root folder of your game client, right next to your main client.exe
  2. Open CFF Explorer: Launch CFF Explorer and drag-and-drop your game client.exe into the program.
  3. Go to Import Adder: On the left panel, click on Import Adder.
  4. Add your DLL: Click the Add button and select your compiled DLL from the client folder.
  5. Import by Name: You will see a list of exported functions. Select the dummy export function (if you didn't change the source code, it should be called protect2024) (you can rename to whatever you want) . Select it, click Import By Name, and then click Add.
  6. Rebuild Import Table: Click the Rebuild Import Table button to finalize the injection.
  7. Save the Client: Go to File > Save (or click the save icon) and overwrite your client .exe.
Now, when you launch your game, it will automatically load your hook DLL, which will in turn load libeay32.dll and start intercepting and decrypting your file loads on the fly!

🛠️ Troubleshooting: "libeay32.dll is missing" Error​

If you try to launch your game and get a system error saying libeay32.dll is missing—even though you placed it right next to the .exe—don't panic. This just means the game executable isn't hooking the OpenSSL dependency automatically.

The Fix: You just need to force the client to load it using the exact same method we used for the hook.

  1. Open your client .exe in CFF Explorer again.
  2. Go to the Import Adder.
  3. Add libeay32.dll.
  4. Select any random exported function from the list, click Import By Name, and hit Add.
  5. Rebuild Import Table and save your .exe.
That's it! The client will now forcefully load the OpenSSL library, and your encryption hook will work perfectly.

📥

What’s up, brother? Been a long time. Glad to see you’re still around.
 
Hey everyone,

Today I'm releasing an encryption source code that I received from a developer friend in Vietnam last year. We used to share a lot of knowledge and experiences, but since disappeared from the scene (we lost contact). Because I miss the guy and the collaboration we had, I've decided to share this source with the community.

To be completely honest, back when we were talking, I was dealing with some heavy paranoia regarding real-life events and ended up misleading him a bit. (thats when i decided visit our be loved game. ) :) So, if you are still out there reading this, buddy—let's get in touch again. I have some good news for the Vietnamese community, so please hit me up.

If you've been around the scene, you will likely recognize this. It is widely used across both Chinese and English servers. Many servers have taken this base and modified it to create their own "custom" versions, but the core mechanics remain the same.

🛡️ A Reality Check on "Proprietary" Protection​

When we talk about proprietary client protection, the actual goal is just to make copy-pasting your assets a little more difficult. It keeps the kiddies away, but let's be realistic: it won't perform miracles against someone whos rly want reverse that.

So far, I have not encountered a single private server in this entire community where the client files couldn't eventually be unpacked. Sometimes it takes longer, but the result is always the same: fully unpacked files.

Because this specific hook decrypts files "on the fly" and drops them to the disk temporarily, someone who knows what they are doing will figure out the magic and grab your assets in about 10 minutes.

⚙️ What's Included & How it Works​

This is a two-part system written in C++:

  1. The Encrypter Tool: Packages your files (local, maps, ui, etc.).
  2. The Client DLL: Hooks CreateFileA to intercept file loads and decrypt them for the client.
  3. Algorithms: It relies on OpenSSL for 1024-bit RSA (to secure the headers/keys) and Windows CryptoAPI for RC4 (for bulk file data). It also features basic Anti-VM and Sandbox detection.

🛠️ Setup Instructions​

You can compile this easily using Visual Studio Community. Just make sure you link the required OpenSSL dependencies properly.

To make this build your own, you must change the following variables:

1. Generate and Replace the RSA Keys:You need to generate your own RSA-1024 key pair.

  • Open Decrypting_a_File.cpp and replace the private_key_str variable with your new private key.
  • Open Encrypting_a_File.cpp and replace the public_key_str variable with your new public key.
2. Match the Hardware/Session String:Both the encryption tool and the client DLL need to share the same base string to communicate properly.

  • Find #define STATIC_HDDSN "Ez*ajzO1gIu4W|{y+b^x+xN=~vhM:"
  • Change that random string to something unique, and ensure it matches perfectly in both the Tool source and the dllmain.cpp (local.dll) source.

⚠️ Pro-Tips for Packing​

Your magic and your security rely on your own personal secrets. You can split the keys into multiple pieces, modify the hook logic, etc.

However, do not pack the entire compiled DLL globally with a protector. If you throw the whole binary into Themida or VMP and just click protect, you are going to cause massive performance overhead and likely crash the client. Instead, you need to use a hybrid approach—target and virtualize/mutate only the specific, critical sections of the code that handle the key generation and decryption logic.

Note: I will not be providing support on how to pack or obfuscate your binaries.

I might provide a more detailed tutorial soon, but if you run into basic compilation problems, post them here and I can try to help you out.

View attachment 300926

View attachment 300928

💉 Injecting the DLL (CFF Explorer)​

For the client to actually use your new encryption hook, you need to force the game executable to load it on startup. We will do this by adding it to the client's Import Table.

Requirements: You will need CFF Explorer.


Instructions:

  1. Move your files: Once you compile the project, take your compiled DLL (e.g., local.dll or whatever you named it) and the OpenSSL dependency (libeay32.dll). Place both of them in the root folder of your game client, right next to your main client.exe
  2. Open CFF Explorer: Launch CFF Explorer and drag-and-drop your game client.exe into the program.
  3. Go to Import Adder: On the left panel, click on Import Adder.
  4. Add your DLL: Click the Add button and select your compiled DLL from the client folder.
  5. Import by Name: You will see a list of exported functions. Select the dummy export function (if you didn't change the source code, it should be called protect2024) (you can rename to whatever you want) . Select it, click Import By Name, and then click Add.
  6. Rebuild Import Table: Click the Rebuild Import Table button to finalize the injection.
  7. Save the Client: Go to File > Save (or click the save icon) and overwrite your client .exe.
Now, when you launch your game, it will automatically load your hook DLL, which will in turn load libeay32.dll and start intercepting and decrypting your file loads on the fly!

🛠️ Troubleshooting: "libeay32.dll is missing" Error​

If you try to launch your game and get a system error saying libeay32.dll is missing—even though you placed it right next to the .exe—don't panic. This just means the game executable isn't hooking the OpenSSL dependency automatically.

The Fix: You just need to force the client to load it using the exact same method we used for the hook.

  1. Open your client .exe in CFF Explorer again.
  2. Go to the Import Adder.
  3. Add libeay32.dll.
  4. Select any random exported function from the list, click Import By Name, and hit Add.
  5. Rebuild Import Table and save your .exe.
That's it! The client will now forcefully load the OpenSSL library, and your encryption hook will work perfectly.

📥

Thank you for share. I need these documents.
 
can someone re-upload the source code? the link is not working..
 
can someone re-upload the source code? the link is not working..
 
Is there any big shot who can share the source code of client.exe?
 
Hey guys,

Does anyone still have a working copy of the Client Encryption Source (Tool + Hook DLL) – RSA1024/RC4?

The Google Drive link in the thread seems to be dead now. When I try to open it, Google says the file is unavailable because it violated their Terms of Service.

If the original uploader still has the source, could you please re-upload it somewhere and share a new link?

And if anyone else downloaded it before and still has a copy, I'd really appreciate it if you could share it or point me to a working mirror.

Thanks a lot! 🙏
 

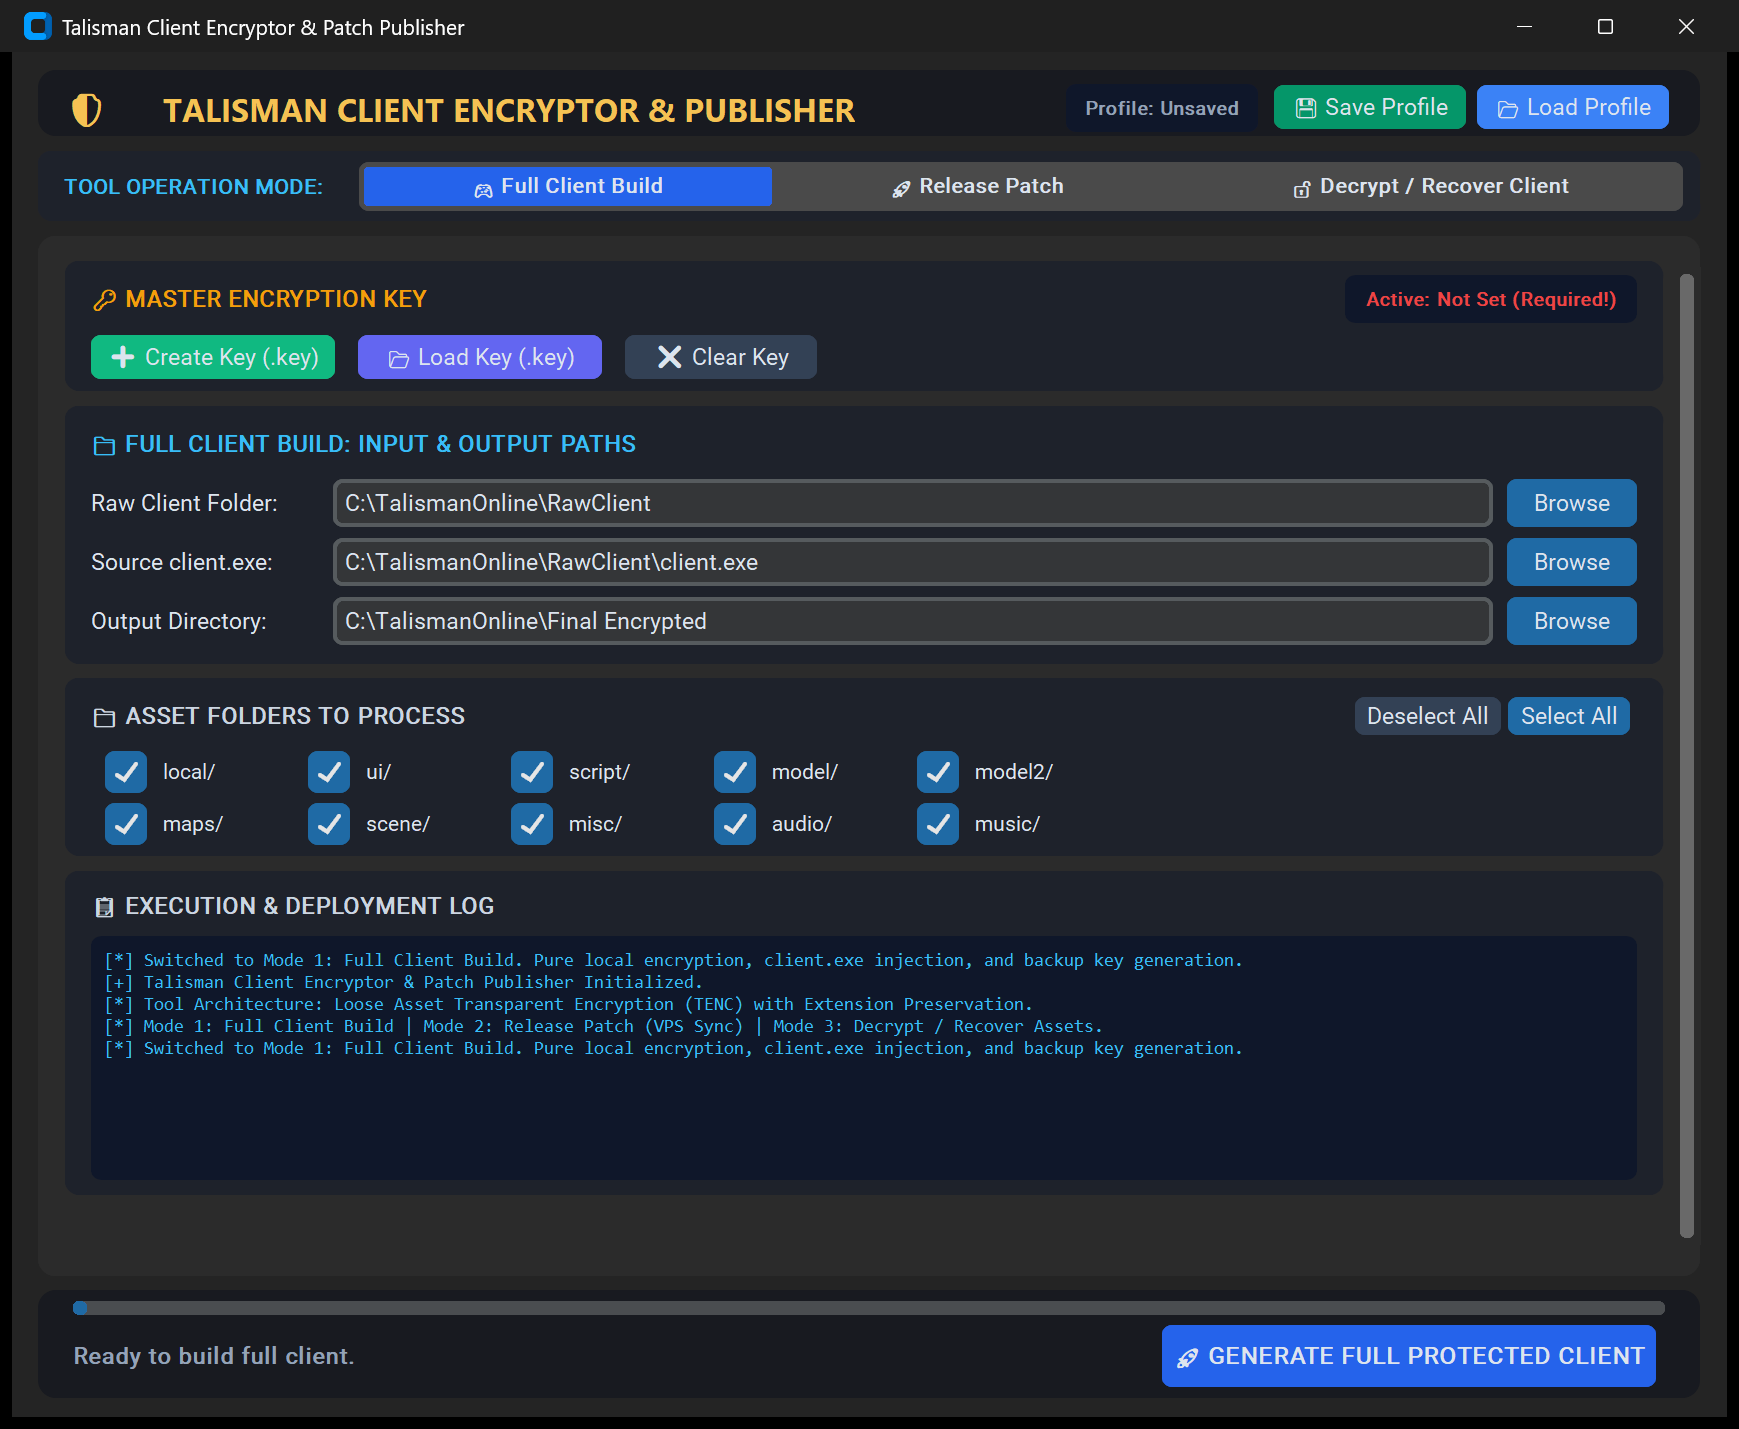
Try This You Will No Need To Do Anything Manually just select decrypted client folder and it will do the rest and you will need to create password and keep it safe coz once you forgot the password it will not gonna recover the file its 2 step of encryption .key+password so if you leack your key then not to worry coz they still need password
 
Back