Website by Leandro-Iron

Search in index.php this:
PHP:
<div class="jqb_slides">
                <div class="jqb_slide" title="'.$rbanner['TituloBan'].'" >
                 <a href="'.$rbanner['LinkBan'].'" target="_blank">
                  <img src="'.$rbanner['ImgBan'].'" height="179" width="522"/>
                 </a>
                </div>
and change it to this:
PHP:
<div class="jqb_slides">
                <div class="jqb_slide" title="'.$rbanner['TituloBan'].'" >
                  <img src="'.$rbanner['ImgBan'].'" height="179" width="522"/>
                </div>
This will completely remove link function from the slider.

Thanks that is good.Now i will try to seach and se how to give it a value like in php with "else" so when it has a link to work and when not to work.
 
i have more 3 errors in usercp.
Warning: mssql_query() [function.mssql-query]: message: Invalid object name 'CabalCash.dbo.Bank'. (severity 16) in C:\xampp\htdocs\cabalonline\sisGeral.php on line 123

Warning: mssql_query() [function.mssql-query]: Query failed in C:\xampp\htdocs\cabalonline\sisGeral.php on line 123

Warning: mssql_fetch_row(): supplied argument is not a valid MS SQL-result resource in C:\xampp\htdocs\cabalonline\sisGeral.php on line 124
i will try to fix them asap ,but sure if some1 solved already them ill be glad to hear how ?ty
 
Last edited by a moderator:
Edit: I didnt checked enough close for first time. So theres a missconfiguration in your config file.
That db should be CashShop.

PHP:
define('DB_CCA','CABALCASH');
define('DB_CSH','CASHSHOP');

I think on your config the DB_CSH is defined as CabalCash instead of CashShop. :8:

$ck_cash = mssql_query("SELECT Alz FROM ".DB_csh.".dbo.Bank WHERE UserNum='".$IdxAcc."'");

to replace DB_CSH with ?
thanks in advice:drool:

EDIT : I CHANGED AS YOU SAID AND STILL THE SAME ERROR ,look :


W
arning: mssql_query() [function.mssql-query]: message: Invalid object name 'CASHSHOP.dbo.Bank'. (severity 16) in C:\xampp\htdocs\cabalonline\sisGeral.php on line 123
 
Did you run chumpy's CashShop querys? Without them dont wonder why this error appears. :lol:

PROBLEM FIXED !

THANKS IN ADVICE (ERRORS GONE)

P.S : FOR ALL WHO WILL GET THOSE ERROR ONLY RUN THIS IN NEW QUERY(CashShop)

CREATE DATABASE cashshop
GO
USE cashshop
GO

CREATE TABLE [dbo].[Bank] (
[UserNum] [int] NOT NULL ,
[Alz] [bigint] NOT NULL
) ON [PRIMARY]
GO

CREATE TABLE [dbo].[ShopItems] (
[Id] [int] IDENTITY (1, 1) NOT NULL ,
[Name] [varchar] (50) COLLATE Chinese_PRC_CI_AS NOT NULL ,
[Description] [varchar] (200) COLLATE Chinese_PRC_CI_AS NOT NULL ,
[ItemIdx] [int] NOT NULL ,
[DurationIdx] [int] NOT NULL ,
[ItemOpt] [int] NOT NULL ,
[Image] [varchar] (200) COLLATE Chinese_PRC_CI_AS NOT NULL ,
[Honour] [int] NULL ,
[Alz] [int] NULL ,
[Category] [int] NOT NULL ,
[Available] [int] NOT NULL
) ON [PRIMARY]
GO

SET QUOTED_IDENTIFIER OFF
GO
SET ANSI_NULLS OFF
GO


CREATE PROCEDURE SetBankAlz( @UserNum int, @Alz bigint)
AS
BEGIN
BEGIN TRAN
IF NOT EXISTS( SELECT UserNum
FROM Bank
WHERE UserNum = @UserNum )
BEGIN
INSERT Bank (UserNum, Alz)
VALUES ( @UserNum, 0)
END
ELSE
BEGIN
UPDATE Bank
SET Alz = @Alz
WHERE UserNum = @UserNum
END
COMMIT TRAN
END


GO
SET QUOTED_IDENTIFIER OFF
GO
SET ANSI_NULLS ON
GO

SET QUOTED_IDENTIFIER ON
GO
SET ANSI_NULLS OFF
GO

CREATE PROCEDURE [dbo].[GetBankAlz]( @UserNum int ) AS
BEGIN
if ( SELECT UserNum FROM Bank WHERE UserNum = @UserNum ) is Null
BEGIN
INSERT Bank ( UserNum, Alz)
VALUES( @UserNum, 0)
END
SELECT UserNum, Alz
FROM Bank
WHERE UserNum = @UserNum
END

GO
SET QUOTED_IDENTIFIER OFF
GO
SET ANSI_NULLS ON
GO

:sleep: PeAcE ! :sleep:


EDIT : SOME1 KNOW AND HAVE A GOOD CC SHOP AND ALZ SHO FOR THIS WEBSITE?WHEN I AM CLIKING ON CASHSHOP ITS REDIRECTING ME IN 404 PAGE NOT FOUND,THANKS XD

-------Make Your Own WebSite More Secured------------
There are several methods to make your login script secure. The most crucial step for that is obviously to escape strings using real_escape_string() function that varies from the PHP version. This will get you rid of some common SQL injection attacks via form or address bar.

Another thing you must make secure is the user password. When talking about PHP and database, anything that comes in our mind is md5 hashing and password encryption. The most basic step we use is to encrypt the user password while registering in the internet.

For example,

md5($password);

This will generate the md5 hash of any value replaced by the variable password. However the MD5 hashing is most secure since 1991 there are still some tools that keeps record of hashes of most dictionary words. For example, MD5decrypter.com.

For example try decrypting 5f4dcc3b5aa765d61d8327deb882cf99 in MD5decrypter.com

This will clearly show you an decrypted form of the hash : password.

This means that some common dictionary words can be decrypted because most people use dictionary words or easy to remember words as their passwords. Only few of them considers creating confusing but memorable password.

But using some tweaks in MD5 hash, you can encrypt the has with your own little algorithm. For example, using salts.

$salt = “theSecurePass”;
$userpass = $_POST['pass'];
$md5pass = md5($salt . $userpass);

Using salts will redfine the algorithm of md5 hashing which is pretty much secure than usual md5 hashing.

But you must keep in mind that the $salt must be much more secured and not detectable.

Incase if you want another capsule of security you can add your own algorith to the salted MD5 hashes. This can be done by changing and replacing or swapping the values.

For example,

If the normal salted hash is 5f4dcc3b5aa765d61d8327deb882cf99 and some how the hacker get to know your salt then still you can have another layer of security.

5f4dcc3b5aa765d61d8327deb882cf99 can be replaced to 9965b5aa75f4dcc3d61882cf7deb

Notice how the bold characters are arranged.

To bring this to life I’ve used the function mb_substr(). The syntax is mb_substr($string, [starting character position number], [length of character].

Using mb_substr(myvalue, 3, 4) will select alue.

Use this technique wisely in your salted MD5 has as the following code does.
$salt = "mypassword";
$userpass = "a";
$md5pass = md5($salt . $userpass);
$value1 = mb_substr($md5pass, 3, 12);
$value2 = mb_substr($md5pass, 22, 7);
$value3 = mb_substr($md5pass, 8, 13);
$md5 = $value1 . $value2 . $value3;


you can make it more complex and un-decodable until and unless your server is secure from external attacks.
 
Last edited:
Come on... This is not a PHP help forum, and you're cluttering up this guy's thread. Posts deleted. Take it somewhere else.
 
Hi guys i need some help!

Warning: session_start() [function.session-start]: Cannot send session cookie - headers already sent by (output started at C:\Xampp\htdocs\configuracao\confCabal.php:1) in C:\Xampp\htdocs\index.php on line 10

Warning: session_start() [function.session-start]: Cannot send session cache limiter - headers already sent (output started at C:\Xampp\htdocs\configuracao\confCabal.php:1) in C:\Xampp\htdocs\index.php on line 10

what is this problem i cant know what i do now :S
 
Can you tell us where are the news stored ? I want to delete them from php file.
 

Attachments

  • aaaa - Website by Leandro-Iron - RaGEZONE Forums
    aaaa.webp
    110.7 KB · Views: 179
Dont want to be of topic but i like how you make him try ti understand the construction of the site.
To be more explicite then Acna in that code you can se that the query is selecting the last 4 news (.dbo.CADNOTICIAS) from the database (.DB_ACC.) and the display order is by the database field CodMens

I think now it very clear yes?
 
Hi guys i need some help!

Warning: session_start() [function.session-start]: Cannot send session cookie - headers already sent by (output started at C:\Xampp\htdocs\configuracao\confCabal.php:1) in C:\Xampp\htdocs\index.php on line 10

Warning: session_start() [function.session-start]: Cannot send session cache limiter - headers already sent (output started at C:\Xampp\htdocs\configuracao\confCabal.php:1) in C:\Xampp\htdocs\index.php on line 10

what is this problem i cant know what i do now :S


<?php ob_start(); ?> <--- put this code on top of ConfCabal.php
 
I want to make a recover password function on this site.Does anyone know a good tutorial on making this or where should i start.
 
I want to make a recover password function on this site.Does anyone know a good tutorial on making this or where should i start.

To make the system password recovery, you need to make a function that generates a new random password for the player, because the passwords are fully encrypted in MD5.
In fact it would not be "password recovery" but "new Password Generator."

One tip I can offer is to use this little function.

$Newpwd = substr(md5(mktime()),0.8);

This will generate 8 random letters or numbers for the player.

The best method of sending data via email is the "SMTP", research it and succeed.
Good luck


$Newpwd = substr(md5(mktime()),0.8);
try to connect it to email of the user/player so that when they change password they can use their email to recover it the code for it is in the forum , you can search it "error" .
 
I have found a "bug".
The Confirm donations sistem doesent work
I am going to explai detailed right now
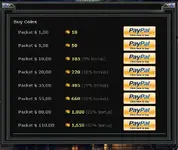
I seted up the site to use the paypal system so users can donate/purchase with money coins

So o user choses to buy some coins
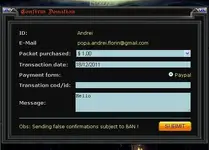
He will go here
1 - Website by Leandro-Iron - RaGEZONE Forums

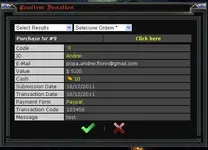
After that he will have to Confirm the purchase
2 - Website by Leandro-Iron - RaGEZONE Forums

so an site admin will Aprove it or denie it if the tranfer is succesfull or not
3 - Website by Leandro-Iron - RaGEZONE Forums

If the admin confirms it the cahs is not given to the user as it should be.Normal that should be the functions.So i checked the file structure and i found in the sisConfirmDonate.php from the _administrador folder of the site that the mssql query does not insert any data in the CabalCash database where the coins(in my case) are stored.
here is the query
PHP:
if($_POST['sbmtConf']) {
$txtCod = $_POST['txtCod'];
	$sql = "UPDATE ".DB_ACC.".dbo.CADDONATE Set 
                  ckEntrega = 1,
				  DataEntr = getdate(),
				  RespEntr = '".$txtLogin."'
                  where CodDon  = '".$txtCod."'";
			    $sql_result = mssql_query($sql);
	 echo '<script>alert(\'Donation successfully confirmed !\'); location=\'sisConfirmDonate.php\'</script>'; 
mssql_close();
	}

To make this work it must insert in the databse CabalCash in the field Alz and to the correct UserNum.
I tried some ways but couldnt make it work.
I would apreciate some help.
Thanks
 
Back